Understand the operating environment
Build visibility across control assets, engineering stations, remote access, communications, dependencies, and ownership.
Explore OT assessments →SCADA · ICS · OT cybersecurity
Industrial cyber risk reaches beyond data. We connect digital exposure to physical operations, engineer safe corrective action, and verify that controls reduce risk without compromising the process.
Cybersecurity for engineered systems
Priorities reflect safety, production, recoverability, access paths, vendor support, and the equipment actually deployed.
Build visibility across control assets, engineering stations, remote access, communications, dependencies, and ownership.
Explore OT assessments →Prioritize vulnerabilities and strengthen zones, conduits, identities, vendor paths, monitoring, and compensating controls.
Explore vulnerability management →Coordinate with operations and engineering, test safely, preserve evidence, and document residual operational risk.
Explore operational readiness →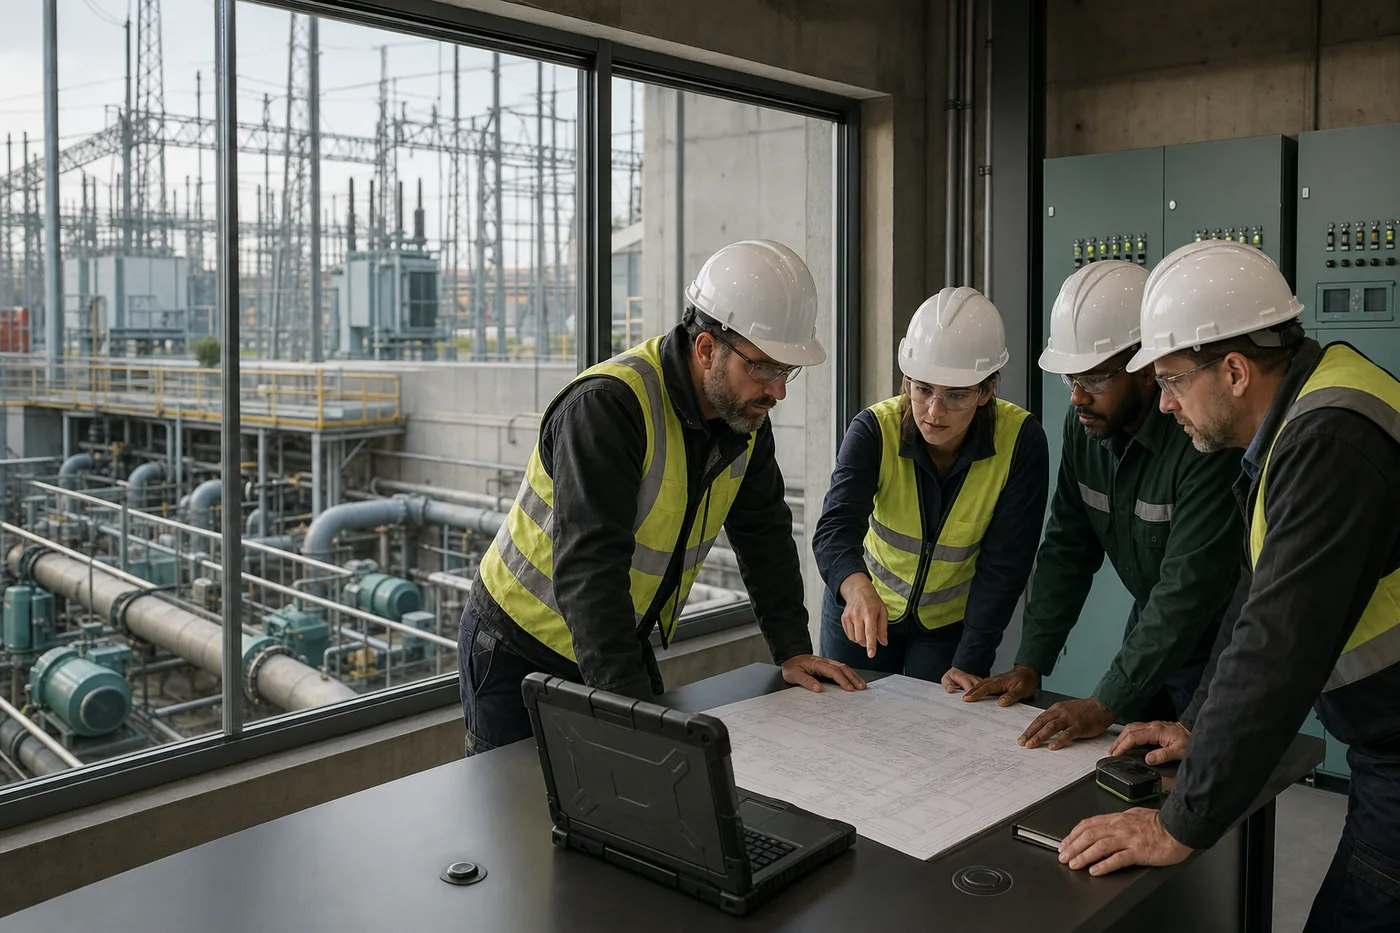
Infrastructure-scale coordination
SCADA Cyber helps teams work through the boundary between technology and operations. The result is a plan that respects the process, assigns accountable owners, and can be verified under controlled conditions.
SCADA intelligence
The National Institute of Standards and Technology (NIST) has issued the initial public draft of SP 800-82r4, updating guidelines for Operational Technology (OT) security with…
Read the analysis →
Four critical vulnerabilities in Rockwell Automation RSLinx Classic (versions <= 4.50) could allow remote attackers to crash the service using crafted CIP packets, disrupting communication…
Read the analysis →
Two vulnerabilities in FactoryTalk Historian Machine Edition could allow authenticated attackers to execute remote code or cause a system crash via the web interface.
Read the analysis →Defense across the control path
Control privileged access, remote sessions, vendors, and trust crossing into operations.
Limit pathways and monitor communications between business, operations, and control layers.
Protect projects, logic, firmware, workstations, baselines, and authorized change.
Prepare restoration, replacement dependencies, manual procedures, and validation evidence.
Discuss your risks, priorities, and next steps for stronger safeguards.